
Room4.01Floor 4 Security and backup
Cybersecurity
Endpoint protection, email filtering and multi-factor sign-in for GTA offices, set up and supported by one team. We also work through cyber insurance forms and PIPEDA breach steps with you.
- Endpoint protection
- Email filtering
- Multi-factor sign-in
- Insurance forms and PIPEDA steps
Security for an office without a security team
For most offices of 5 to 250 people, good security is a short list done properly: protection on every computer, filtering on every mailbox, multi-factor sign-in on every account and a backup of your Microsoft 365 data. Our managed plan includes all four, set up and supported by the technicians who answer your help desk calls.
The calls we get are rarely dramatic. A staff member clicked a link and typed in their password. A mailbox started sending fake invoices to clients overnight. An insurer’s renewal form asks whether MFA is on for every account, and nobody is sure. Each of these is cheaper to prevent than to clean up.
Security runs through our other services too. Firewalls and remote access are covered on the networks and firewalls page, and backups of servers and files on backup and disaster recovery. This page covers the security tools in the monthly plan and the questions insurers and privacy law put to you.
What the managed plan sets up, and what is quoted
The managed plan includes three security tools: endpoint protection on staff computers, filtering on incoming email, and multi-factor authentication set up on staff accounts. Microsoft 365 backup is included too. Work beyond that, such as a firewall replacement or fixing gaps found on an insurance form, is quoted as a fixed project before it starts.
Endpoint protection
Security software on every staff computer blocks known malware and flags programs that behave suspiciously. If it blocks something and a staff member is worried, they call the help desk and a technician checks the machine.
Email filtering
Phishing email is one of the most common ways attackers get into small businesses. Filtering catches much of the phishing, malicious attachments and spoofed senders before they reach an inbox. Nothing catches everything, so staff can forward anything odd to the help desk and ask before they click.
Multi-factor authentication
MFA means a stolen password alone is not enough to sign in. We set it up on staff Microsoft 365 accounts, walk people through the authenticator app, and help when someone gets a new phone. Admin accounts deserve the strictest settings of all, since they are the accounts an attacker wants most.
| Security work | Managed plan |
|---|---|
| Endpoint protection on staff computers | Included |
| Email filtering | Included |
| MFA setup on staff accounts, and help when someone changes phones | Included |
| Microsoft 365 backup | Included |
| Help desk calls about a suspicious email, a locked account or an odd pop-up | Included |
| Microsoft 365 licence upgrades for extra security features | Billed separately |
| Firewall hardware and its security subscriptions | Billed separately |
| Insurance gap fixes, written security policies and other security projects | Fixed quote |
Not on the managed plan? Help with a security problem is available as hourly support, with the rate given on request, and security projects are quoted at a fixed price. The monthly plan’s per-user range is on the pricing page.
What cyber insurance questionnaires ask about
Cyber insurance applications and renewals ask about the same few controls: multi-factor authentication, backups and how email is protected. Many also ask about patching, admin accounts and whether you have an incident response plan. We go through the form with you, check each answer against what is actually set up, and quote anything that needs fixing first.
- MFA. Insurers usually want it on email, on remote access such as VPN, and on admin accounts. “Most staff” and “every account” are different answers, and the form will ask which one is true.
- Backups. Expect questions on how often you back up, whether a copy is kept offline or apart from your network, and when a restore was last tried. If nobody has tried one, say so.
- Email controls. Filtering, warnings on messages from outside senders, and the domain records (SPF, DKIM and DMARC) that make your domain harder to spoof.
Answer honestly. An insurer can dispute a claim, or try to cancel the policy, when the application described controls that were not in place, so “MFA on all accounts” needs to be true on the day you sign. The plan’s MFA setup, email filtering and Microsoft 365 backup cover a good share of a typical form.
How the plan maps to the Cyber Centre’s baseline controls
The Canadian Centre for Cyber Security publishes 13 baseline controls for small and medium organizations, a practical checklist for offices without security staff.
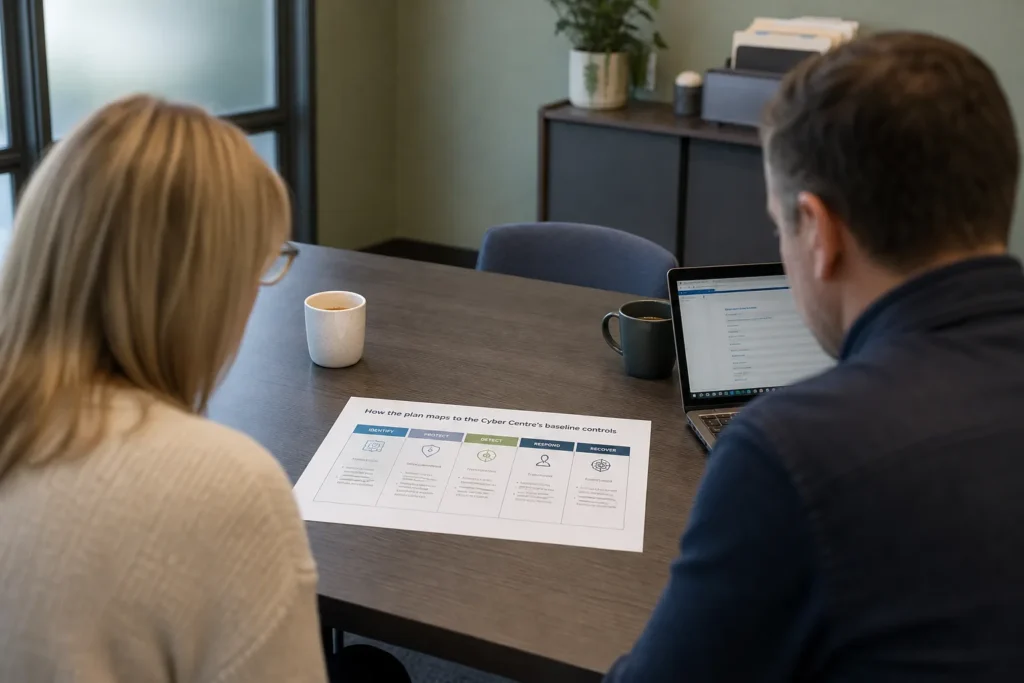
Tools in our managed plan cover parts of three, and our firewall work part of a fourth. We can work through the rest with you. No government body has audited this mapping.
- Enable security software (BC.3). Endpoint protection on staff computers, included in the plan.
- Use strong user authentication (BC.5). MFA setup on staff accounts, included in the plan.
- Backup and encrypt data (BC.7). Microsoft 365 backup is included. Servers and local files are scoped and quoted separately.
- Establish basic perimeter defences (BC.9). A business firewall, supported by the same team. New firewalls are quoted as projects.
Other controls start with a decision from you. An incident response plan (BC.1) is a short document that says who does what when something goes wrong. Employee awareness training (BC.6), secure mobility (BC.8) and access control (BC.12) are policy questions as much as technical ones, and each needs an owner in your office.
PIPEDA breach reporting basics
Under PIPEDA, the federal privacy law that covers most Ontario businesses, you must report a breach of security safeguards to the Privacy Commissioner of Canada when it creates a real risk of significant harm to someone. You must also notify the people affected, and keep a record of every breach for 24 months, reported or not.
Significant harm includes financial loss, identity theft, damage to reputation and humiliation. Whether the risk is real depends on how sensitive the information is and how likely it is to be misused. A lost laptop with an encrypted drive is a very different case from a mailbox full of client tax slips read by a stranger.
We handle the technical side: securing the affected accounts, working out what was exposed as far as the logs allow, and writing down what happened and when, so your breach record has facts in it. The decision to report, and what to say, rests with you and your lawyer or insurer. If it is happening right now, call the 24/7 emergency line and a technician will answer.
Security work quoted as fixed projects
Some security work is a one-off job with a clear end. We scope it, give you a fixed quote, and start once you approve it. Managed plan clients and hourly clients are quoted the same way. Typical projects for GTA offices include insurance gap fixes, email domain records and a written incident response plan.
- Cyber insurance questionnaire review and gap fixesFixed quote
- MFA roll-out for an office not on the managed planFixed quote
- Email domain records: SPF, DKIM and DMARCFixed quote
- Microsoft 365 security settings reviewFixed quote
- Written incident response plan for your officeFixed quote
- Review against the Cyber Centre's 13 baseline controlsFixed quote
Questions people ask
What security controls do cyber insurers require?
Most forms ask about multi-factor authentication on email, remote access and admin accounts, backups kept apart from your network, and email filtering. Many also ask about patching and an incident response plan. Requirements differ by insurer and by policy, so read your own form closely and answer only what is true today.
Is cybersecurity included in your managed plan?
The core tools are. Every managed plan includes endpoint protection, email filtering, MFA setup and Microsoft 365 backup, along with help desk calls about anything suspicious. Firewall hardware, Microsoft 365 licence upgrades and security projects such as insurance gap fixes are billed separately or quoted before work starts.
Do we have to report a cyber attack in Canada?
If personal information was involved and the breach creates a real risk of significant harm, PIPEDA requires you to report it to the Privacy Commissioner of Canada and notify the people affected. Every breach, reported or not, must be recorded and the record kept for 24 months. Your lawyer or insurer can advise on wording.
How does your plan relate to the Canadian Centre for Cyber Security baseline controls?
Tools in our managed plan cover parts of several of the 13 baseline controls, including security software, strong user authentication and backup. That is our own mapping of how we set things up, and no government body has audited or approved it. The remaining controls can be worked through with you as a planning project.
What should we do if someone clicked a phishing link?
Call the help desk straight away. If the computer is behaving strangely, unplug its network cable or turn off its Wi-Fi. A technician will reset the password, check recent sign-ins and mailbox rules, and look over the computer. Outside business hours, the 24/7 emergency line reaches a technician.
Tell us what’s going on
Pick how urgent it is and leave a way to reach you. The help desk replies by phone or email. If work has stopped, call 647-812-3775 instead.
Something broken, or something to plan?
For anything urgent, call. A technician answers the emergency line 24/7. For everything else, open a ticket and tell us what is going on.